vCISO Services · ✅ Verified by Extern · ⏱️ In progress
vCISO Security Risk Assessment Externship
Be a junior security consultant. Find a company's weak spots, score them on NIST and create a deck for senior leaders.
vCISO Services Externship via Extern
vCISO Services Externship via ExternRecent Master's grad with experience managing enterprise systems, privileged access, and network security.
Projects selected from recent security and infrastructure engagements.
vCISO Services · ✅ Verified by Extern · ⏱️ In progress
Be a junior security consultant. Find a company's weak spots, score them on NIST and create a deck for senior leaders.
Hydroficient · Aug 2026 · ✅ Verified by Extern
Build, hack, and defend real IoT infrastructure, then hand your security playbook to an actual company. You’ll launch realistic cyberattacks, from spoofing and replay attacks to unauthorized shutoffs, and implement defenses like TLS and mTLS.
SWBTL LLC · Nov 2025
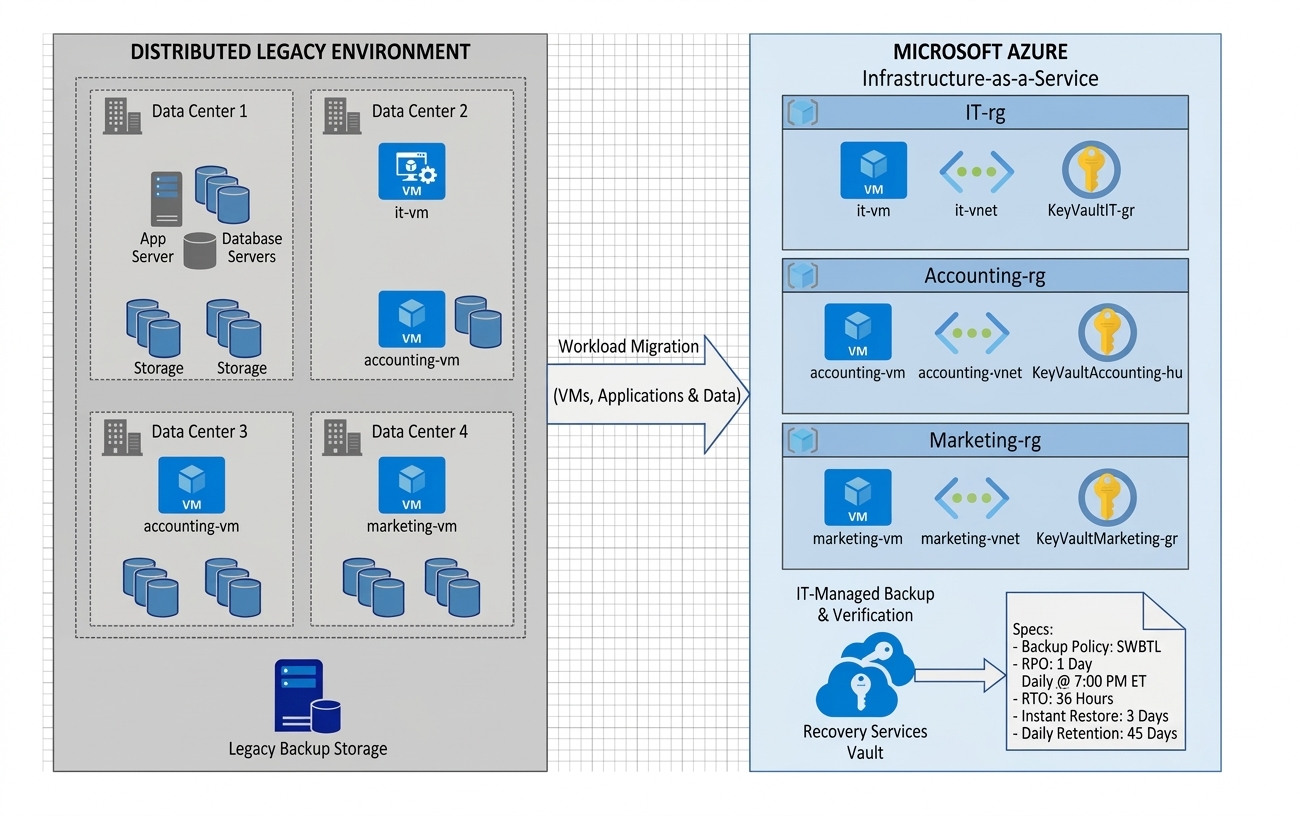
Designed an Azure cloud migration plan to shift corporate workloads out of 4 leased legacy data centers with security and stability risks. Configured RBAC permissions and Key Vault to protect sensitive records.
Target Retail Stores · Aug 2025
Tracked an active attack kill chain from initial penetration to data exfiltration, collecting 12 challenge flags and uncovering the full extent of consumer impact.
Mastercard · May 2025
Designed a phishing email simulation to test employee awareness, analyzed the performance results to pinpoint high-risk business areas, and created a security training presentation to help teams lower organizational risk.
Sep 2024
Delivered a secure ingestion pipeline that drove a 20% improvement in compliance reporting across international business units.
Recent Master's grad with experience managing enterprise systems, privileged access, and network security.
I'm endlessly curious about how systems connect, where vulnerabilities lie, and why technology and sound business practices fail where they should be working together. My studies taught me how attackers use SSL stripping to compromise secure network protocols undetected. So, I worked with Hydroficient to build further skills identifying IoT risks and minimizing attack surfaces. Currently, i'm in a Risk Assessment Externship with vCISO, performing security analysis against NIST CSF 2.0. 🌿When i'm not working toward my career, you'll find me outdoors or falling down a random rabbit hole TMYK.🌿
Externships
vCISO Cybersecurity Risk Assessment Externship
In progress
Education
Western Governors University
Master of Science in Cybersecurity and Information Assurance · Class of 2026
Western Governors University
Master of Science in Information Technology Management · Class of 2024
University at Buffalo
Bachelor of Science in Business Administration, Management Information Systems · Class of 2016
Skills
✅ Verified by Extern · ⏱️ In progress
Be a junior security consultant. Find a company's weak spots, score them on NIST and create a deck for senior leaders.
The externship involved a junior security consultant engagement to assess an organization's security posture. Work included identifying vulnerabilities, mapping them to NIST controls, and preparing findings for senior leadership. Deliverables combined a scored risk register and a presentation deck.

I conducted a targeted client intake, mapped technical and process risks to NIST controls, and produced a scored risk register plus a leadership-facing slide deck summarizing key findings.
✅ Verified by Extern
Build, hack, and defend real IoT infrastructure, then hand your security playbook to an actual company. You’ll launch realistic cyberattacks, from spoofing and replay attacks to unauthorized shutoffs, and implement defenses like TLS and mTLS.
The work examined a hotel water-management system that streamed device telemetry to a cloud dashboard. It mapped components and data flows, applied STRIDE to identify spoofing, tampering, and cloud-dependency risks, and produced a prioritized threat model, tooling, secured MQTT pipeline, experiment results, and an integrated anomaly detector. The work was awarded Top Performer by Hydroficient.
.jpg)
I delivered a suite of security artifacts: a prioritized STRIDE threat model, a sensor telemetry generator with Colab notebooks, an MQTT topic hierarchy, a TLS- and mTLS-secured pipeline with measured tests, a device provisioning policy, a 12-experiment replay comparison, and an Isolation Forest anomaly detector integrated into the dashboard.
SWBTL LLC · Nov 2025
Designed an Azure cloud migration plan to shift corporate workloads out of 4 leased legacy data centers with security and stability risks. Configured RBAC permissions and Key Vault to protect sensitive records.

Built out shared resources into a multi-tenant Azure architecture isolating Accounting, Marketing, and IT departments. ⁕ Enforced strict least-privilege RBAC by mapping dedicated Resource Groups. ⁕ Deployed standalone Azure Key Vaults per department to secure cryptographic keys. ⁕ Standardized business continuity using a centralized Recovery Services Vault for daily automated system backups.
Reinforced NIST SP 800-53 and PCI DSS control compliance. Automated daily 7:00 PM backups to guarantee a 24-hr RPO and 36-hr RTO resilience threshold. This work remediated all cross-departmental access vulnerabilities closing unauthorized access gaps, lowered overall infrastructure risks, and gave technical teams clear, verifiable logs to prove the cloud environment stays secure and audit-ready.
Target Retail Stores · Aug 2025
Tracked an active attack kill chain from initial penetration to data exfiltration, collecting 12 challenge flags and uncovering the full extent of consumer impact.

D1: Traced ransom email ➡️ D2: Geolocated attacker IP ➡️ D3: Found SSTI exploit ➡️ D4: Found LFI leak ➡️ D5: Spotted DNS tunnel ➡️ D6: Extracted stolen CVVs ➡️ D7: Isolated exfil process ➡️ D8: Exposed Git backdoor ➡️ D9: Proved session hijack ➡️ D10: Uncovered leaked creds ➡️ D11: Identified malicious hardware ➡️ D12: Decrypted LUKS partition to unmask persistent reverse SSH tunnel IOC
🏆 Ranked 204 out of 869 international participants, placing in the top 24% overall.
Mastercard · May 2025
Designed a phishing email simulation to test employee awareness, analyzed the performance results to pinpoint high-risk business areas, and created a security training presentation to help teams lower organizational risk.

Served as an analyst on Mastercard’s Security Awareness Team during a security simulation ⁕ Researched common phishing tactics like malicious links and fake attachments ⁕ Crafted a custom test email to evaluate employee detection skills, and built a short training presentation to teach affected business units how to spot and report these threats before they hit the network
Learned how to utilize performance data to find security gaps across different departments. Gained hands-on insight into how other enterprise teams prevent and mitigate phishing attacks. This project highlighted how targeting security training to the right groups directly lowers organizational risk and protects sensitive corporate networks from data theft.
Sep 2024
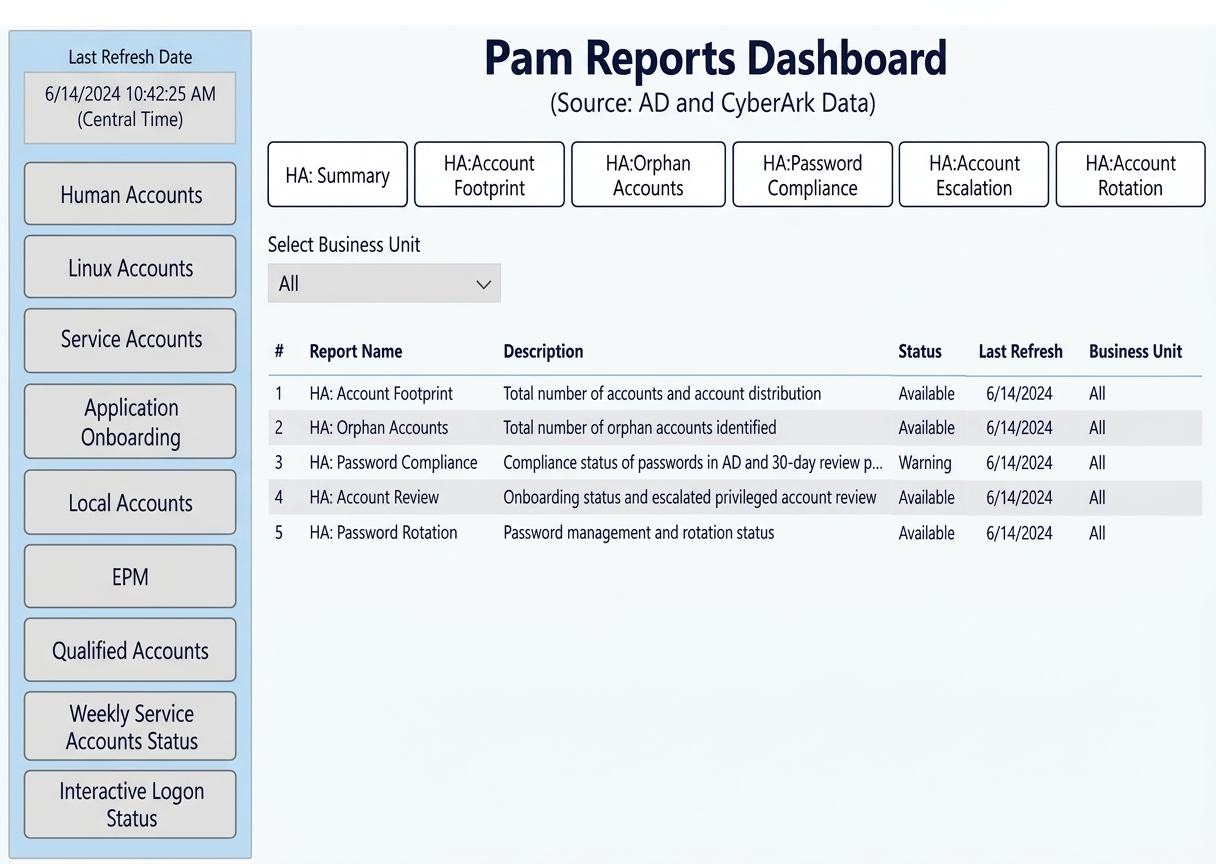
Delivered a secure ingestion pipeline that drove a 20% improvement in compliance reporting across international business units.

🔨 Refactored legacy PowerShell scripts ensuring they matched existing Active Directory attributes📈 Aligned schemas with various Excel reports across changing business units, preventing Power BI ingestion fail 🌎 Consolidated source data (CSV/XLSX, CyberArk) into PBI Desktop, publishing metrics to PBI Service for global cloud availability.
I eliminated operational tracking blind spots by delivering real-time visibility into privileged access management metrics, ensuring continuous audit readiness.